
Your Browsing History
Meet Your Seller

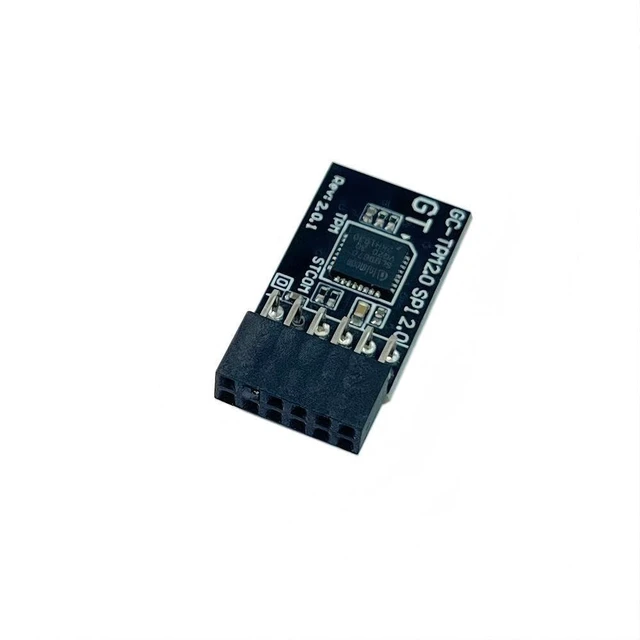
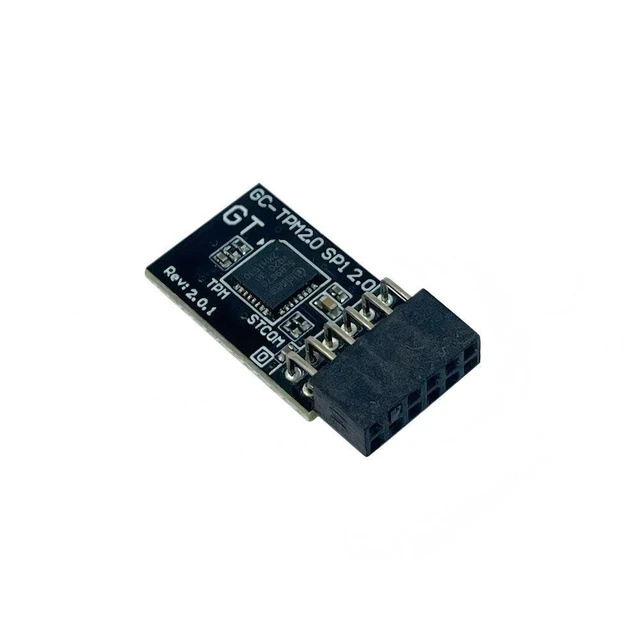
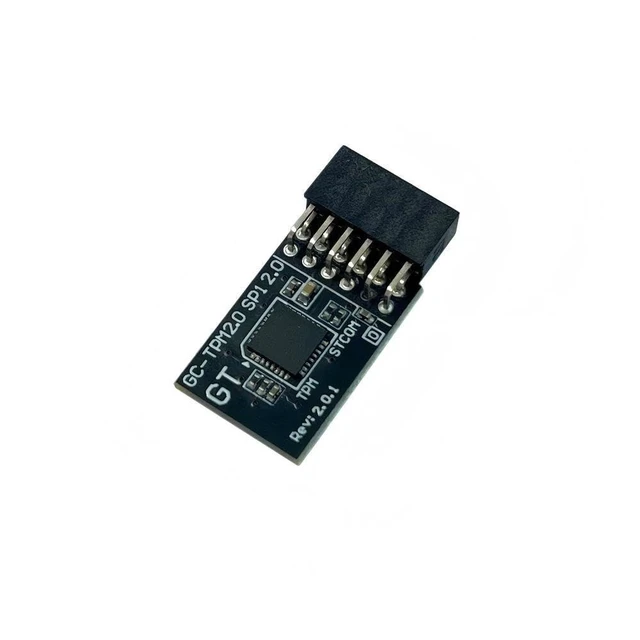


TPM 2.0 Security Module - 12-Pin SPI Interface, Trusted Platform Module for Windows 11 Upgrade, Hardware Encryption Board
- [Windows 11 Upgrade Ready] The ultimate hardware solution for upgrading your desktop PC to Windows 11. It successfully bypasses the OS installation restrictions, allowing older but capable motherboards to meet the strict TPM 2.0 security requirements.
- [12-Pin SPI Interface] Specifically designed for motherboards equipped with a 12-Pin (12-1 pin layout) SPI TPM header. Please verify your motherboard's manual to ensure it uses a 12-Pin SPI interface before purchasing, as LPC or 14-pin/20-pin headers are NOT compatible.
- [Hardware-Level Encryption] Acts as a secure crypto-processor that helps you generate, store, and limit the use of cryptographic keys. Essential for enabling features like BitLocker drive encryption, Windows Hello, and secure boot to protect your sensitive data from hackers.
- [Stable & Reliable Performance] Built with high-quality components and a premium PCB design. It ensures uninterrupted communication between the security chip and your CPU, providing a rock-solid foundation for your PC's security infrastructure.
- [Easy Installation & Setup] Simply plug the module into the designated 12-Pin SPI header on your motherboard when the PC is powered off. Once installed, easily enable the "Discrete TPM" (dTPM) feature within your motherboard's BIOS settings.
+
+
Overview
Specs
Reviews

Any questions? Our AI mode will help you find out quickly.
Try me now
What is a TPM 2.0 Module?
A Trusted Platform Module (TPM) is a dedicated microchip designed to secure your hardware through integrated cryptographic keys. Whether you are safeguarding corporate secrets, enabling BitLocker to encrypt your hard drives, or just wanting to play the latest competitive games that require secure boot, this module has you covered.
CRITICAL BUYER'S WARNING (RMA Prevention):
To avoid compatibility issues, please strictly follow these checks before ordering:
- Pin Count & Protocol Check: This module is STRICTLY for 12-Pin SPI headers. It will NOT fit or work with 14-Pin, 20-Pin, or older LPC protocol headers. Please check your motherboard manual carefully.
- BIOS Configuration: After inserting the module, you must enter the BIOS, disable the CPU's built-in firmware TPM (fTPM / PTT), and explicitly enable the external/discrete TPM.
Key Technical Specifications:
- Module Type: Trusted Platform Module (TPM 2.0)
- Interface / Protocol: SPI (Serial Peripheral Interface)
- Pin Layout: 12-Pin (12-1 configuration)
- Supported OS: Windows 10, Windows 11
- Application: OS Upgrades, BitLocker Encryption, Secure Boot
- Status: Pure Hardware Add-on (Requires BIOS activation)
Warranty & Returns
Warranty, Returns, And Additional Information
Warranty
- Please contact the Seller directly for warranty information. Warranty information may also be found on the Manufacturer's website.
- CONTACT
Return Policies
- Return for refund within: 30 days
- Return for replacement within: non-replaceable
- This item is covered by GeekSpace Return Policy
Manufacturer Contact Info
- For a directory of all our manufacturers, please click below.
- Manufacturers Directory
LOADING...