here!
I’m your shopping assistant for PC builds, upgrades, and everything tech.
Got questions? Ask away!
Start a conversation
here!
I’m your shopping assistant for PC builds, upgrades, and everything tech.
Got questions? Ask away!
Start a conversation



Any questions? Ask CelesteSM will help you find out quickly.
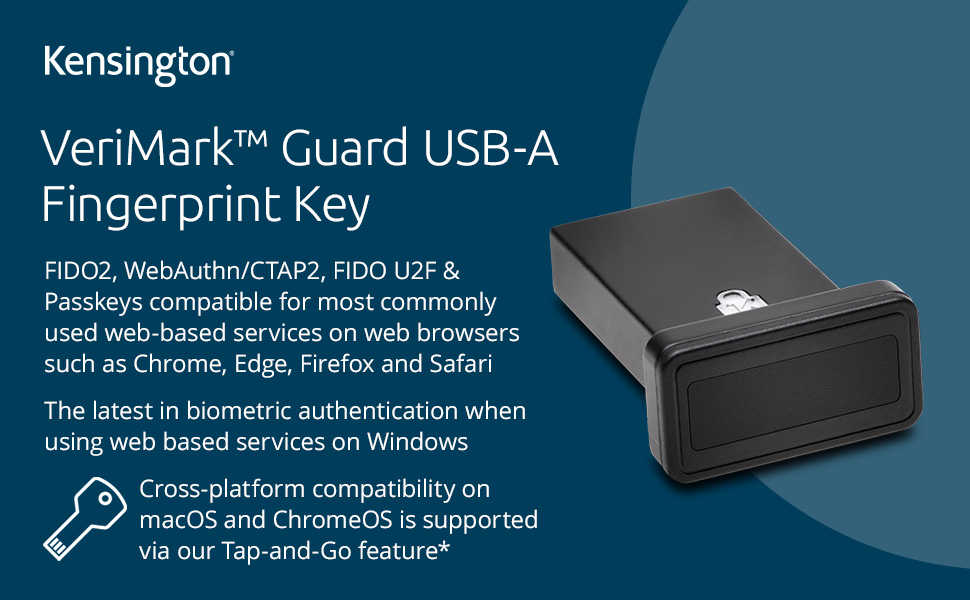
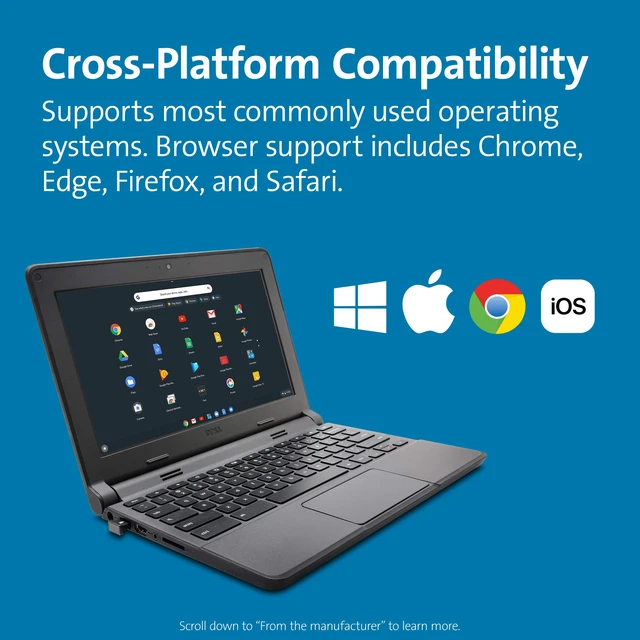
*Cross-platform compatibility for macOS and ChromeOS is supported via our Tap-and-Go feature. For a complete list of authentication services visit VeriMark support site.
**For biometric support on macOS and Chrome OS, users must first configure Windows Hello for Microsoft Services and Dropbox login authentication. Without this configuration, the security key will still work as a Tap-and-Go solution but will not support biometric authentication.
***Tap-and-go combines a username and password with second-factor security key authentication to enable extra security on non FIDO2 services. For services using the older FIDO U2F standard, the user places their finger on the VeriMark Guard for a security token experience (instead of using biometric authentication). See a complete list of services on the VeriMark support site.
Not compatible with Windows Hello or Apple Touch ID
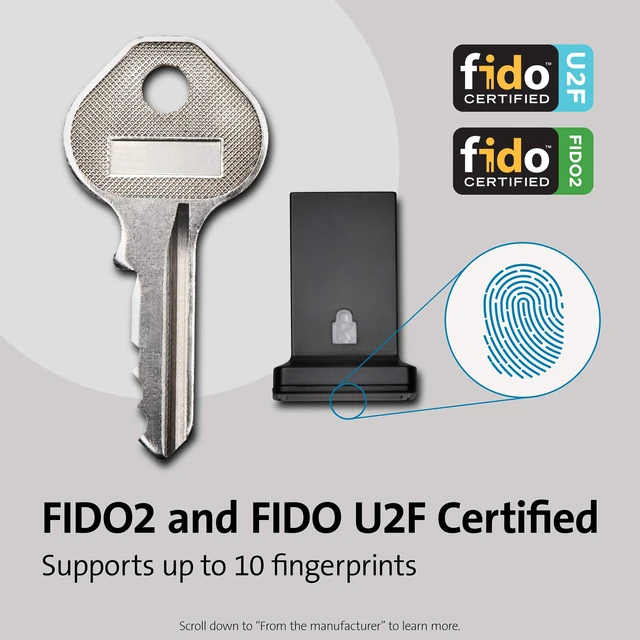
Only certified with FIDO2 version 2.0.
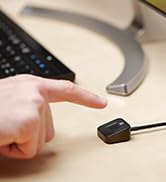
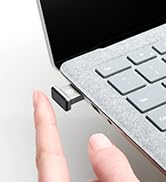
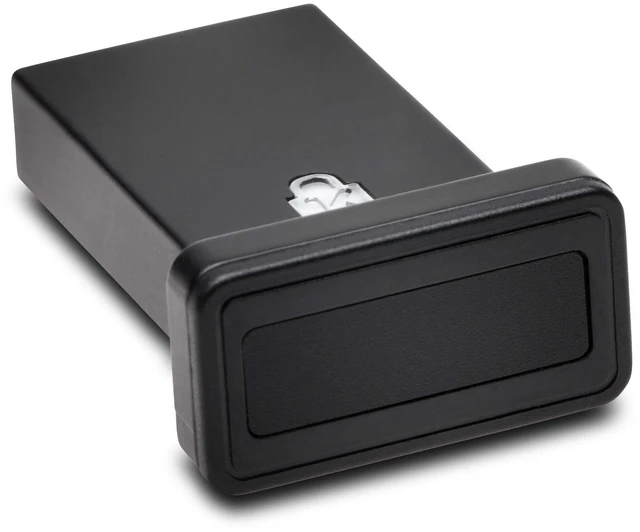
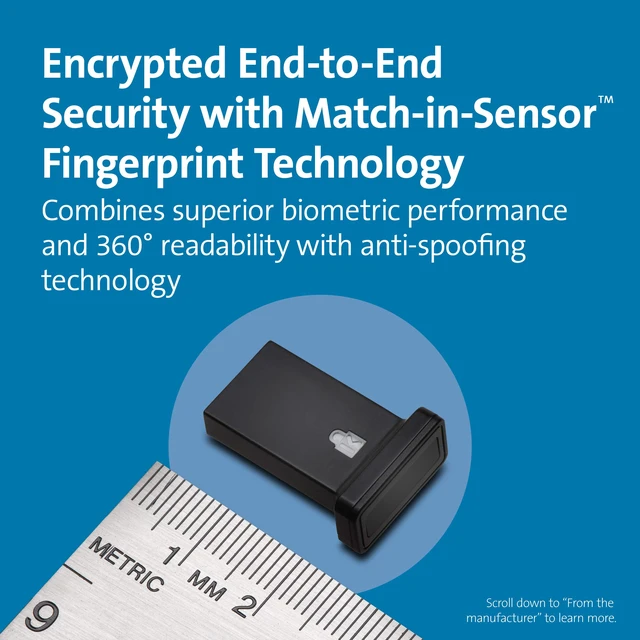
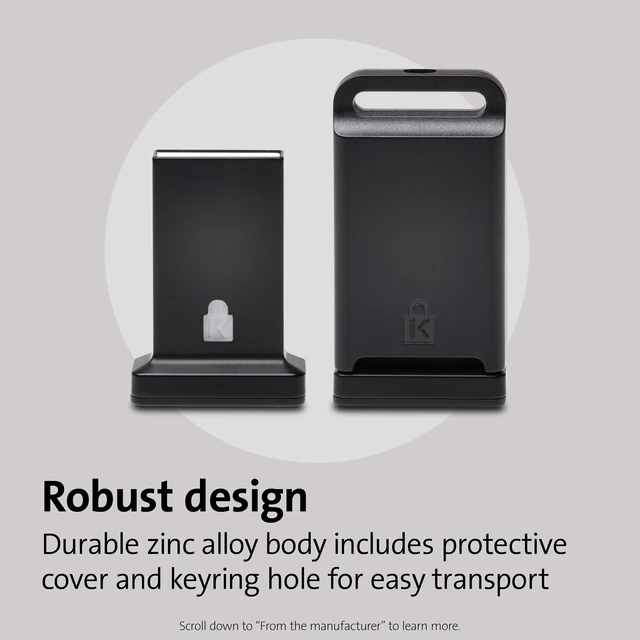
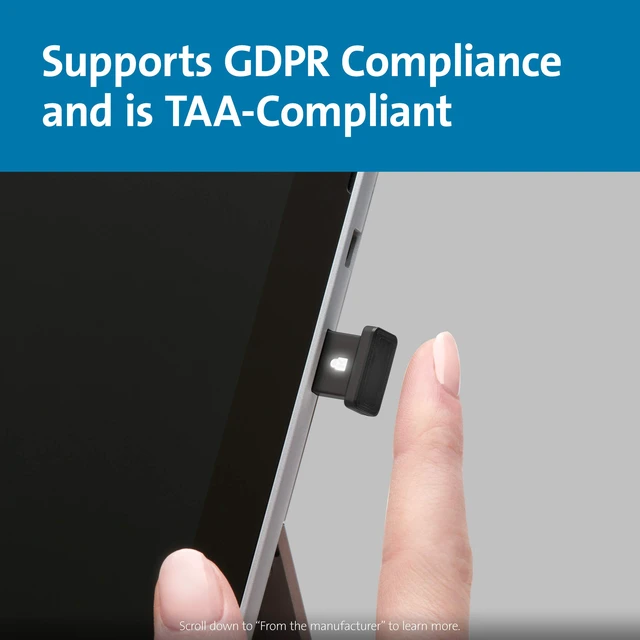
The VeriMark Guard USB-A Fingerprint Key - FIDO2, WebAuthn/CTAP2, & FIDO U2F - Cross Platform offers the latest in biometric authentication. FIDO2 and FIDO U2F certified with expanded authentication options, including strong single-factor (passwordless), dual, multi-factor, and Tap-and-Go for FIDO U2F services. Maximum compatibility with web services including Google, Facebook, and Microsoft (for Windows Hello, refer to VeriMark or VeriMark IT), with support for Chrome, Edge, Firefox, and Safari. Exceeds industry standards for false acceptance rate (FAR) and false rejection rate (FRR). Supports GDPR compliance and is TAA-compliant.
Q: Is it necessary to install driver before using?
A: A driver is necessary for VeriMark, VeriMark IT and VeriMark Desktop for Windows 10 and 11. User can either manually install by downloading the latest driver from our support page and following the step instructions or using the Windows Optional driver install from Synaptics. VeriMark Guard is a plug and play dongle and no drivers are needed.
Q: Where can I download the driver that I need?
A: Drivers can be downloaded from our official site support page: kensington.com/software/verimark-setup/ by selecting the device and following the installation instructions.
Q: What's the difference between manual and optional driver?
A:
Q: What should I do if VeriMark couldn't recognize my device? (Unknown device issue)
A: Unknown device issue is simply a unrecognized peripheral connected to the host. In order to fix this issue the user has to install the drivers for VeriMark using one of the methods explained on the support page.
Q: How to solve error code 10 issue?
A: Error 10 is generated when Device Manager can't start the hardware device, usually caused by outdated or corrupted drivers. Reinstalling the latest drivers may solve the issue.
 VeriMark Guard USB-A |  VeriMark Desktop |  VeriMark IT |  VeriMark Guard USB-C |  VeriMark | |
|---|---|---|---|---|---|
| Customer Reviews | — | — | — | — | — |
| Price | — | — | — | — | — |
| Best for | Personal/office/Enterprise/Desktop computers | Personal/office/Enterprise/Desktop computers | Office/Enterprise | Personal/office/Enterprise | Home/Office |
| FIDO | FIDO U2F certified, FIDO2/WebAuth, compatible | FIDO U2F certified, FIDO2/WebAuth, compatible | FIDO2/WebAuth Compatible for Multi factor and password less authentication | FIDO U2F certified ,FIDO2/WebAuth, CTAP2 certified | FIDO U2F Certified for Universal 2nd Factor Authentication |
| Windows Security login | Cross platform OS , U2F security key (Tap-and-Go) Microsoft service account login as security key (no Windows Hello) | Windows Hello & Windows Hello for Business certified, U2F security key (Tap-and-Go) | Windows Hello & Windows Hello for Business certified | Cross platform OS , U2F security key (Tap-and-Go) Microsoft service account login as security key (no Windows Hello) | Windows Hello certified |
| False Rejection Rate (FRR) | 2% | 2% | 2% | 2% | 3% |
| False Acceptance Rate (FAR) | 0.001% | 0.001% | 0.001% | 0.001% | 0.002% |
| Fingerprint Technology | Synaptics FS7600 (Match-in-sensor) | Synaptics FS7600 (Match-in-sensor) | Synaptics FS7600 (Match-in-sensor) | Synaptics FS7600 (Match-in-sensor) | Synaptics FS4300 (Match-on-host) |
| USB Data Encryption | •AES-256/SHA-256 Elliptic Curve Cryptography for key exchange, authentication, and data validation with unique keys for every sensor •AES-256/HMAC-SHA-256 authenticated encryption for credential and template data wrapping | •AES-256/SHA-256 Elliptic Curve Cryptography for key exchange, authentication, and data validation with unique keys for every sensor •AES-256/HMAC-SHA-256 authenticated encryption for credential and template data wrapping | •AES-256/SHA-256 Elliptic Curve Cryptography for key exchange, authentication, and data validation with unique keys for every sensor •AES-256/HMAC-SHA-256 authenticated encryption for credential and template data wrapping | •AES-256/SHA-256 Elliptic Curve Cryptography for key exchange, authentication, and data validation with unique keys for every sensor •AES-256/HMAC-SHA-256 authenticated encryption for credential and template data wrapping | •AES-256/SHA-256 •SSLv3 for secure session establishment •RSA-2048 public key cryptography for key exchange, authentication, and data validation •Match on Host |
| Material | Robust Metal Material (Zinc alloy) Cable length: 3.9 foot (1.2M) | Robust Metal Material (Zinc alloy) Cable length: 3.9 foot (1.2M) | Zinc Alloy | Robust Metal Material (Zinc alloy) & Plastic USB-cap | Plastic & Plastic USB-cap |
| Operating System and browsers support | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •Microsoft Edge •Mozilla Firefox •Google Chrome | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •Microsoft Edge •Mozilla Firefox •Google Chrome | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •Microsoft Edge •Mozilla Firefox •Google Chrome | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •macOS 10.15 (or later) •Chrome OS •Microsoft Edge •Mozilla Firefox •Google Chrome | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •Microsoft Edge •Mozilla Firefox •Google Chrome |
*Cross-platform compatibility for macOS and ChromeOS is supported via our Tap-and-Go feature. For a complete list of authentication services visit VeriMark support site.
**For biometric support on macOS and Chrome OS, users must first configure Windows Hello for Microsoft Services and Dropbox login authentication. Without this configuration, the security key will still work as a Tap-and-Go solution but will not support biometric authentication.
***Tap-and-go combines a username and password with second-factor security key authentication to enable extra security on non FIDO2 services. For services using the older FIDO U2F standard, the user places their finger on the VeriMark Guard for a security token experience (instead of using biometric authentication). See a complete list of services on the VeriMark support site.
Not compatible with Windows Hello or Apple Touch ID
Only certified with FIDO2 version 2.0.
The VeriMark Guard USB-A Fingerprint Key - FIDO2, WebAuthn/CTAP2, & FIDO U2F - Cross Platform offers the latest in biometric authentication. FIDO2 and FIDO U2F certified with expanded authentication options, including strong single-factor (passwordless), dual, multi-factor, and Tap-and-Go for FIDO U2F services. Maximum compatibility with web services including Google, Facebook, and Microsoft (for Windows Hello, refer to VeriMark or VeriMark IT), with support for Chrome, Edge, Firefox, and Safari. Exceeds industry standards for false acceptance rate (FAR) and false rejection rate (FRR). Supports GDPR compliance and is TAA-compliant.
Q: Is it necessary to install driver before using?
A: A driver is necessary for VeriMark, VeriMark IT and VeriMark Desktop for Windows 10 and 11. User can either manually install by downloading the latest driver from our support page and following the step instructions or using the Windows Optional driver install from Synaptics. VeriMark Guard is a plug and play dongle and no drivers are needed.
Q: Where can I download the driver that I need?
A: Drivers can be downloaded from our official site support page: kensington.com/software/verimark-setup/ by selecting the device and following the installation instructions.
Q: What's the difference between manual and optional driver?
A:
Q: What should I do if VeriMark couldn't recognize my device? (Unknown device issue)
A: Unknown device issue is simply a unrecognized peripheral connected to the host. In order to fix this issue the user has to install the drivers for VeriMark using one of the methods explained on the support page.
Q: How to solve error code 10 issue?
A: Error 10 is generated when Device Manager can't start the hardware device, usually caused by outdated or corrupted drivers. Reinstalling the latest drivers may solve the issue.
VeriMark Guard USB-A | VeriMark Desktop | VeriMark IT | VeriMark Guard USB-C | VeriMark | |
|---|---|---|---|---|---|
| Customer Reviews | — | — | — | — | — |
| Price | — | — | — | — | — |
| Best for | Personal/office/Enterprise/Desktop computers | Personal/office/Enterprise/Desktop computers | Office/Enterprise | Personal/office/Enterprise | Home/Office |
| FIDO | FIDO U2F certified, FIDO2/WebAuth, compatible | FIDO U2F certified, FIDO2/WebAuth, compatible | FIDO2/WebAuth Compatible for Multi factor and password less authentication | FIDO U2F certified ,FIDO2/WebAuth, CTAP2 certified | FIDO U2F Certified for Universal 2nd Factor Authentication |
| Windows Security login | Cross platform OS , U2F security key (Tap-and-Go) Microsoft service account login as security key (no Windows Hello) | Windows Hello & Windows Hello for Business certified, U2F security key (Tap-and-Go) | Windows Hello & Windows Hello for Business certified | Cross platform OS , U2F security key (Tap-and-Go) Microsoft service account login as security key (no Windows Hello) | Windows Hello certified |
| False Rejection Rate (FRR) | 2% | 2% | 2% | 2% | 3% |
| False Acceptance Rate (FAR) | 0.001% | 0.001% | 0.001% | 0.001% | 0.002% |
| Fingerprint Technology | Synaptics FS7600 (Match-in-sensor) | Synaptics FS7600 (Match-in-sensor) | Synaptics FS7600 (Match-in-sensor) | Synaptics FS7600 (Match-in-sensor) | Synaptics FS4300 (Match-on-host) |
| USB Data Encryption | •AES-256/SHA-256 Elliptic Curve Cryptography for key exchange, authentication, and data validation with unique keys for every sensor •AES-256/HMAC-SHA-256 authenticated encryption for credential and template data wrapping | •AES-256/SHA-256 Elliptic Curve Cryptography for key exchange, authentication, and data validation with unique keys for every sensor •AES-256/HMAC-SHA-256 authenticated encryption for credential and template data wrapping | •AES-256/SHA-256 Elliptic Curve Cryptography for key exchange, authentication, and data validation with unique keys for every sensor •AES-256/HMAC-SHA-256 authenticated encryption for credential and template data wrapping | •AES-256/SHA-256 Elliptic Curve Cryptography for key exchange, authentication, and data validation with unique keys for every sensor •AES-256/HMAC-SHA-256 authenticated encryption for credential and template data wrapping | •AES-256/SHA-256 •SSLv3 for secure session establishment •RSA-2048 public key cryptography for key exchange, authentication, and data validation •Match on Host |
| Material | Robust Metal Material (Zinc alloy) Cable length: 3.9 foot (1.2M) | Robust Metal Material (Zinc alloy) Cable length: 3.9 foot (1.2M) | Zinc Alloy | Robust Metal Material (Zinc alloy) & Plastic USB-cap | Plastic & Plastic USB-cap |
| Operating System and browsers support | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •Microsoft Edge •Mozilla Firefox •Google Chrome | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •Microsoft Edge •Mozilla Firefox •Google Chrome | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •Microsoft Edge •Mozilla Firefox •Google Chrome | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •macOS 10.15 (or later) •Chrome OS •Microsoft Edge •Mozilla Firefox •Google Chrome | •Windows 10 OS 19H1 (or later) •Windows 11 OS 21H2 (or later) •Microsoft Edge •Mozilla Firefox •Google Chrome |