
Your Browsing History
- Free 30-day Returns
$70.99
Meet Your Seller

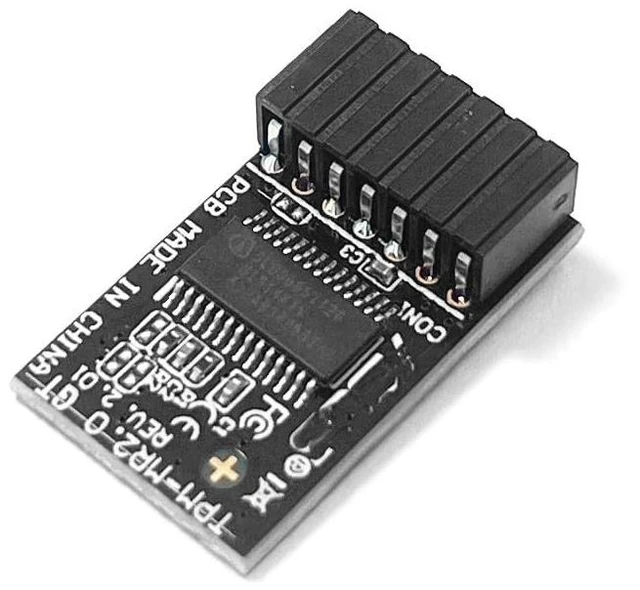
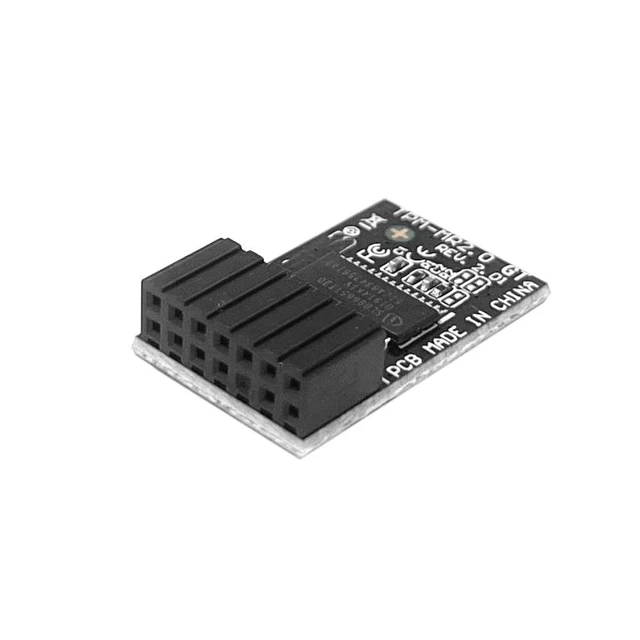
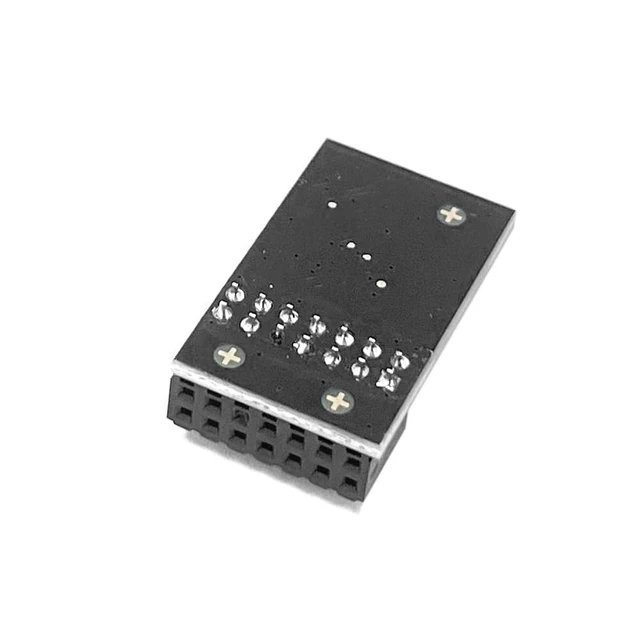
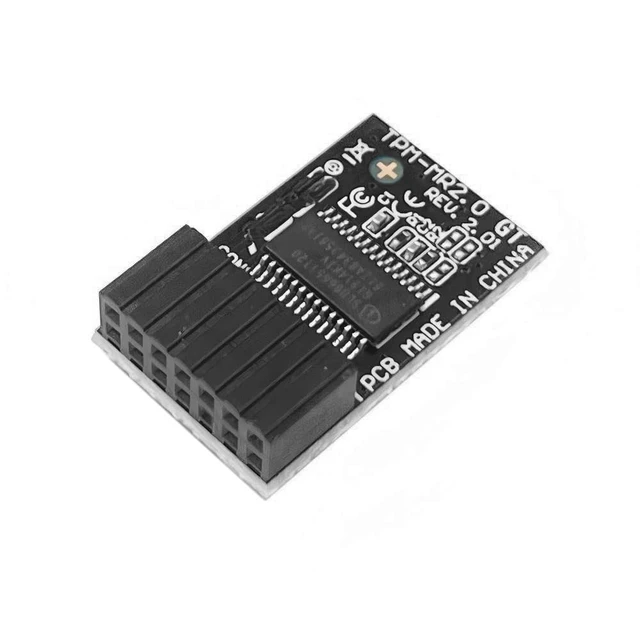
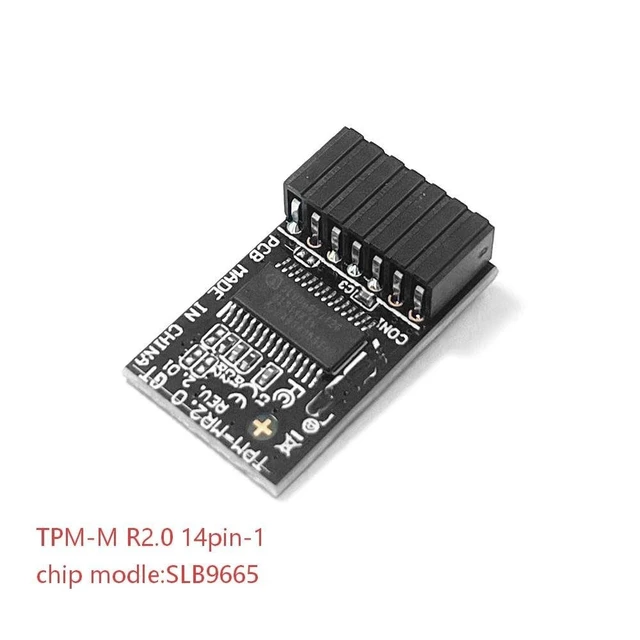


TPM 2.0 Module TPM LPC 14PIN SLB9665 for ASUS ROG Crosshair VI Hero
- TPM-M R2.0 Module LPC 14pin-1 with Infineon SLB9665 Replacement for ASUS ROG Motherboard Crosshair VI HERO ROG Crosshair VI HERO (WIFI AC) ROG Rampage V EDITION 10 ROG Zenith II Extreme Alpha
- Compute Securely Bus Header Key Compatible with ASUS ROG Maximus IX EXTREME ROG Maximus XI HERO (WIFI) ROG Maximus X APEX ROG Maximus IX HEROROG MAXIMUS IX CODEROG MAXIMUS IX APEXROG MAXIMUS IX FORMULA
- Important: The minimum hardware requirements for upgrading to Windows 11 via TPM 2.0 are as follows: 1 GHz or faster 64-bit processor (dual-core/multi-core), 4 GB of memory, 64 GB of storage space, firmware that supports UEFI Secure Boot and TPM 2.0, DirectX 12-compatible graphics card, and a display with a resolution of 720p or higher.
- Purpose a: Resolve the TPM 2.0 verification issue when upgrading to Windows 11, enabling it to function as an independent encryption chip, providing secure storage for sensitive data, and enhancing security;
- Use b: Hardware encryption acceleration,
+
+
Overview
Specs
Reviews

Any questions? Our AI mode will help you find out quickly.
Try me now
Compatible models: for ASUS Motherboard TPM Trusted Platform ModuleROG Maximus IX EXTREMEROG Maximus XI HERO (WIFI) ROG Maximus X APEXROG Maximus IX HEROROG MAXIMUS IX CODEROG MAXIMUS IX APEXROG MAXIMUS IX FORMULAROG Crosshair VI HEROROG Crosshair VI HERO (WIFI AC) ROG Rampage V EDITION 10ROG Zenith II Extreme AlphaCompatible with TPM-M R 2.014 pin-1
Chipset: Infineon
SLB9665PIN DEFINE:
14PinInterface: LPC
Important Notes: 1. This product is only compatible with older motherboards such as Intel and AMD. It is not compatible with newer motherboard models featuring firmware TPM, all-in-one PCs, or laptops. 2. The minimum hardware requirements for upgrading to Windows 11 via
TPM 2.0 are as follows: a 1 GHz or faster 64-bit processor (dual-core/multi-core), 4 GB of memory, 64 GB of storage space, firmware supporting UEFI Secure Boot and TPM 2.0, a DirectX 12-compatible graphics card, and a display with a resolution of 720p or higher. 3. This product has a 14pin-1 connector. Please carefully check the pin positions in the image to ensure compatibility with your motherboard before purchasing.
Core Applications:
1: Seamless upgrade to
Windows 11: Resolve TPM 2.0 verification issues and easily upgrade to the latest operating system.
2: Enhanced
hardware-level security: Provides an independent secure encryption chip specifically designed for securely storing sensitive data (such as encryption keys, digital certificates, and login credentials), thereby enhancing overall system security.
3: Hardware
encryption acceleration: Reduces CPU load by accelerating encryption operations via dedicated hardware, indirectly improving system response speed and enhancing the smooth operation of certain encryption-dependent applications (such as games and security software). How to select and install a security module: 1. Confirm whether the host has TPM 2.0 or if TPM 2.0 is enabled. 2.
Click Run,
enter: tpm. msc (Win+R keys), and check if the TPM version is ready. 3. If version 2.0 is displayed but not ready, you need to configure settings in the BIOS; consult the motherboard manufacturer's customer service. 4. Open the host and inspect the TPM pins on the motherboard. 5. When installing the module, ensure the chip-side faces inward, align with the pins, and insert fully to prevent loosening. (See image for direction)
Chipset: Infineon
SLB9665PIN DEFINE:
14PinInterface: LPC
Important Notes: 1. This product is only compatible with older motherboards such as Intel and AMD. It is not compatible with newer motherboard models featuring firmware TPM, all-in-one PCs, or laptops. 2. The minimum hardware requirements for upgrading to Windows 11 via
TPM 2.0 are as follows: a 1 GHz or faster 64-bit processor (dual-core/multi-core), 4 GB of memory, 64 GB of storage space, firmware supporting UEFI Secure Boot and TPM 2.0, a DirectX 12-compatible graphics card, and a display with a resolution of 720p or higher. 3. This product has a 14pin-1 connector. Please carefully check the pin positions in the image to ensure compatibility with your motherboard before purchasing.
Core Applications:
1: Seamless upgrade to
Windows 11: Resolve TPM 2.0 verification issues and easily upgrade to the latest operating system.
2: Enhanced
hardware-level security: Provides an independent secure encryption chip specifically designed for securely storing sensitive data (such as encryption keys, digital certificates, and login credentials), thereby enhancing overall system security.
3: Hardware
encryption acceleration: Reduces CPU load by accelerating encryption operations via dedicated hardware, indirectly improving system response speed and enhancing the smooth operation of certain encryption-dependent applications (such as games and security software). How to select and install a security module: 1. Confirm whether the host has TPM 2.0 or if TPM 2.0 is enabled. 2.
Click Run,
enter: tpm. msc (Win+R keys), and check if the TPM version is ready. 3. If version 2.0 is displayed but not ready, you need to configure settings in the BIOS; consult the motherboard manufacturer's customer service. 4. Open the host and inspect the TPM pins on the motherboard. 5. When installing the module, ensure the chip-side faces inward, align with the pins, and insert fully to prevent loosening. (See image for direction)
Warranty & Returns
Warranty, Returns, And Additional Information
Warranty
- Please contact the Seller directly for warranty information. Warranty information may also be found on the Manufacturer's website.
- CONTACT
Return Policies
- Return for refund within: 30 days
- Return for replacement within: 30 days
- This item is covered by CloudBeast Return Policy
Manufacturer Contact Info
- For a directory of all our manufacturers, please click below.
- Manufacturers Directory
LOADING...